

Priverion Platform
The Priverion platform automates ROPA, DPIA, risk registers and audit workflows for companies and corporate groups. Hosted in Switzerland, ISO 27001-ready and compatible with the FADP (DSG), GDPR and ISO/IEC 27001:2022.
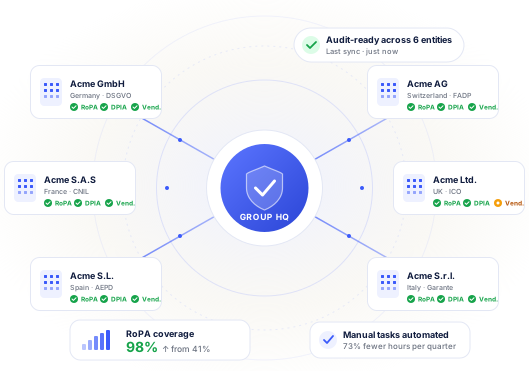
Measurable results for compliance teams.
What customers of the Priverion platform typically see in the first twelve months.
One logic. Three steps.
The platform follows a simple principle, from documentation through governance to responding to incidents and changes.
Document
A single place for your data protection and InfoSec programme. From the records of processing activities (ROPA) through the process-based risk view to the InfoSec asset register, all risks mapped, all evidence in one location.
Manage
Manage assessments, audits and reviews. Generate risk reports based on standards or on the requirements of your organisational units, down to individual subsidiaries.
Respond & Resolve
Respond to incidents, assess notification obligations and manage corrective measures as tasks or projects. Your compliance programme stays up to date and audit-ready at all times.
All compliance topics in a single interface.
From gap analysis through the records of processing activities (ROPA) to audit evidence collection, one platform, one data model, one tenancy model for group structures.
ROPA, records of processing activities
Per Art. 30 GDPR and Art. 12 FADP. Maintained at group level with one-click recertification and versioning per legal entity.
DPIA, data protection impact assessment
Workflow-supported assessment with automatic preliminary risk evaluation. Response-driven follow-up tasks for high-risk processing.
Risk register
Process-based. Assessment, mitigation and audit trail, linked to ROPA, DPIA and assets. Reports by standard or business unit.
Asset Register
InfoSec inventory, classification and ownership. The bridge between data protection and ISO 27001 Annex A.
Vendors & processors
Assessments, DPA tracking and recurring reviews. 100% coverage instead of only critical suppliers.
Workflows & automations
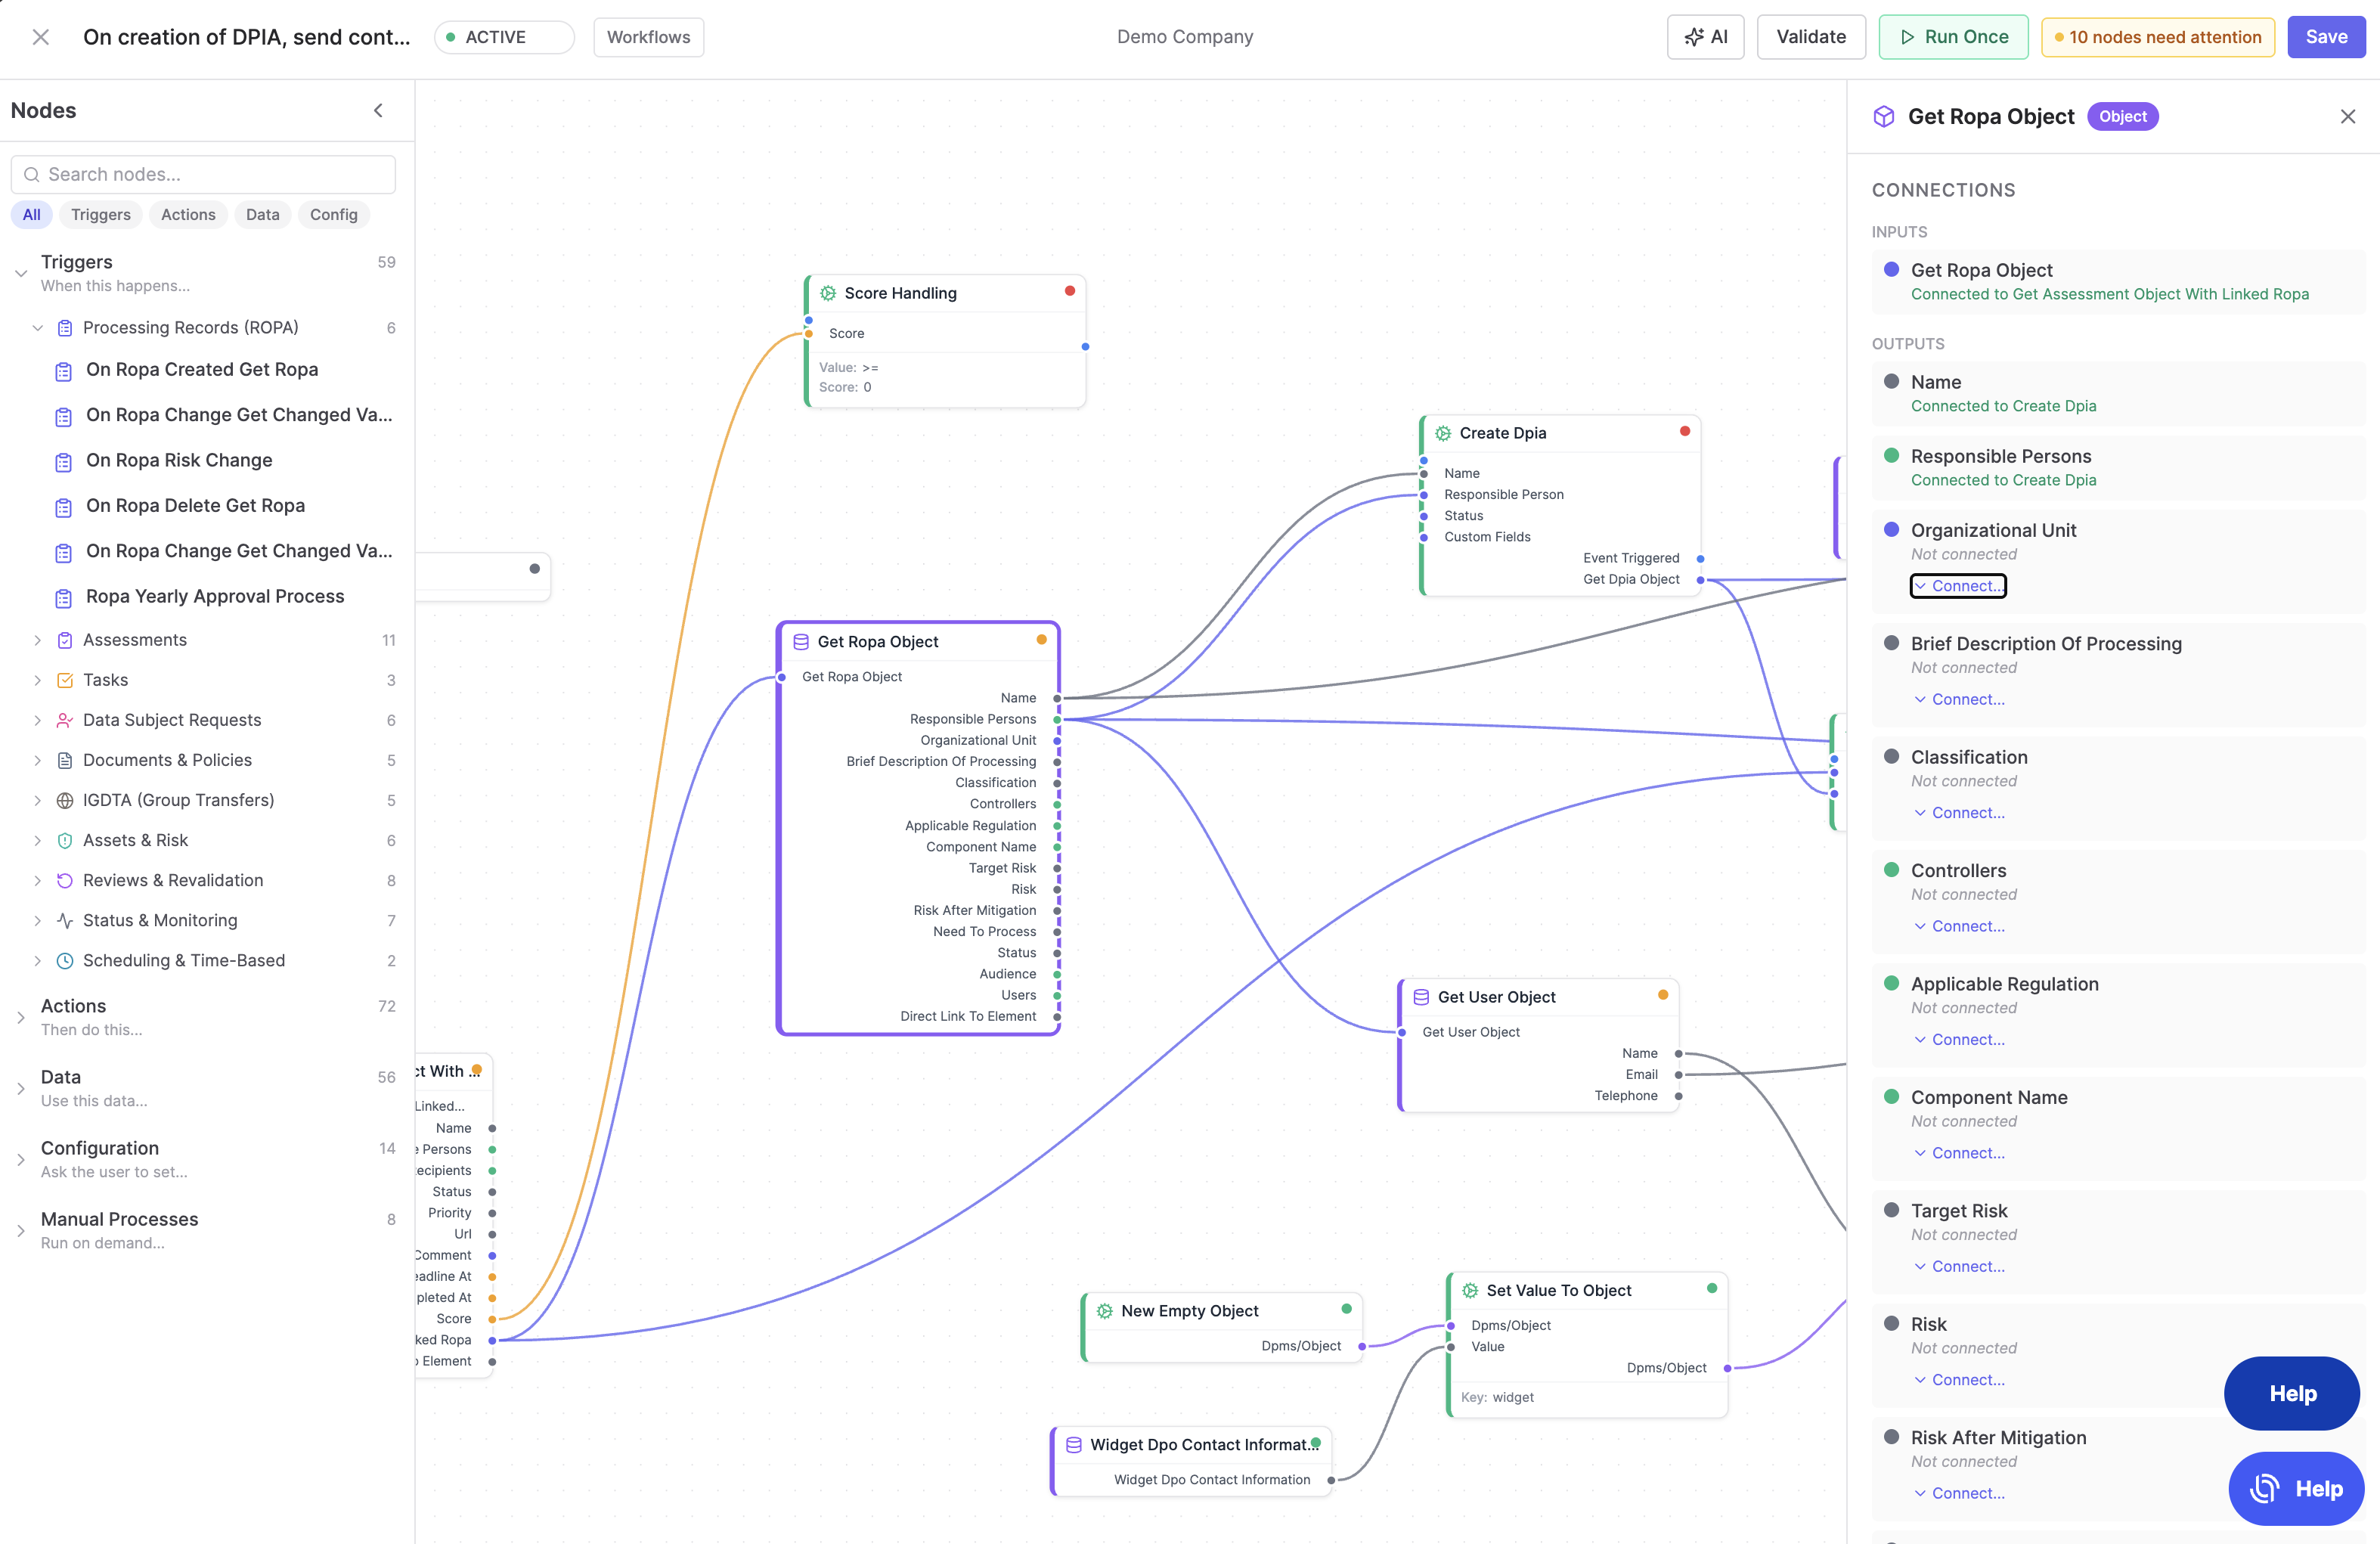
Response-driven follow-up tasks, reminders and escalation. Configurable without code, your existing compliance process, mapped one-to-one.
Group management
Multiple legal entities in a single tenancy model. Changes propagate across entities on demand with a single click.
AI Assist
Gap detection in compliance documentation, risk suggestions and natural-language compliance chat. AI as a co-pilot, not a black box.
What sets Priverion apart.
Four capabilities that make the difference for regulated companies, international groups and Swiss SMEs.
Swiss hosting + data residency
Managed Kubernetes in Switzerland. Data does not leave Switzerland, unless explicitly configured with standard contractual clauses (SCC).
Time Machine
Restore compliance states as of any reference date, evidentially relevant for audits, regulatory inquiries and legal disputes.
Enterprise SSO included
SAML, SCIM, Microsoft Entra ID, Okta, at no additional cost and with no enterprise-tier surcharge. RBAC for group and tenant roles out of the box.
Group-ready, not an SME stopgap
Modelled for groups with five to fifty or more legal entities. Inter-group transfers, shared templates and granular access rights.
In use by compliance teams in regulated industries.
More than 50 data protection and security teams in 14 countries work with the platform, from SMEs to large corporations.
How do we get started with the Priverion platform?
From the initial consultation to productive use typically within four to six weeks. Parallel operation alongside your existing system is possible.
Free initial consultation
Fifteen minutes to clarify your needs with a senior advisor. No obligation, confidential.
Demo & gap analysis
Around one hour of the live platform, tailored to your use case and your compliance programme.
Written quote
Within 24 hours, a fixed price based on the number and size of units. All modules included, except AI credits.
Contract & setup
Data processing agreement with a professional secrecy clause. Onboarding runs in parallel with your existing system.
Data migration
Migration from Excel or your existing DPMS tool as part of a 30-day migration trial, ROPA, templates, assessments and vendor data.
Demo in 30 minutes, in German or English.
A senior advisor will show you the platform using your compliance programme as an example, including an impression of the gap analysis and a migration path.