

Data protection and information security from a single team.
External DPO, EU and UK Representative, ISO 27001, penetration tests and workshops, for SMEs and corporate groups in Switzerland, the EU and the UK.

Our services
Two areas, one accountability: legal compliance and technical security, from a single team.
Industries
Sector-specific compliance & securityHealthcare
For hospitals, practices, EPR communities and MedTech: revised FADP, EPR law, EU AI Act, NIS2/critical-infrastructure reporting and ISO 27001, legally led and multilingual.
Learn moreB2B SaaS providers
For B2B SaaS vendors who want to win enterprise deals: ISO 27001, SOC 2, DPA, pen tests and a vCISO-run trust center that answers security questionnaires fast.
Learn moreFinancial services providers
For banks, insurers, FinTechs and asset managers: FINMA resilience, DORA, ICT risk management, third-party risk and ISO 27001, legally led and multilingual.
Learn moreData Protection
Swiss DSG · EU GDPR · UK GDPR · EU AI ActData Protection Advisors (Switzerland)
For SMEs that need a qualified point of contact under the revised Swiss FADP, without hiring in-house.
Learn moreFADP Compliance (project)
For SMEs that want to bring their data processing into revised-DSG compliance: audit, documentation and training at a fixed fee.
Learn moreData Protection Officers (EU)
For companies required to appoint a DPO under Art. 37 GDPR, onboarded within two weeks.
Learn moreEU Representative (Art. 27 GDPR)
For non-EU companies with EU customers, we receive regulator and data-subject requests on your behalf.
Learn moreUK Representative (UK GDPR)
For providers processing UK personal data without a UK establishment, mandatory representation post-Brexit.
Learn moreAI Officer
For companies that use AI and need responsible AI governance under the EU AI Act without creating a full-time position.
Learn moreAI Governance Check
For companies that want to know where they stand on AI compliance and which measures are needed in what order.
Learn moreData Protection Workshop (SME)
For teams building privacy capability in-house, one day, on-site or remote.
Learn moreInformation Security
ISO 27001 · NIS2 · DORA · AI SecurityNIS2 Consulting
For Swiss companies that supply EU customers: applicability analysis, gap analysis, ISMS and incident reporting, with management's personal liability in mind.
Learn moreISMS (ISO 27001) consulting
For SaaS and mid-market companies on the path to certification, from gap analysis to audit support.
Learn morePenetration test
For SaaS and enterprises with audit or customer requirements, web, network, API.
Learn moreAI Security
For SaaS providers and corporations that build or deploy AI features and must demonstrably secure their LLM, RAG and agent systems.
Learn moreISO 42001 AI Governance
For companies with shadow AI: a turnkey AI management system (AIMS) under ISO 42001, documented and auditable.
Learn moreVulnerability Scan
For a fast first view of exposed attack surfaces, automated, with expert triage.
Learn moreCISO / ISO / ISM
For companies outsourcing security accountability, fractional or as an ongoing mandate.
Learn moreIT security workshop (SME)
For SME IT teams without a dedicated CISO, hands-on, NIS2-ready, in one day.
Learn moreHow we work
Lean, transparent, fast. From intro call to mandate in two weeks.
Intro call
30 minutes, free and non-binding, with Dr. Staiger or a senior consultant.
Scoping & quote
Same-business-day quote with transparent terms, mandate, project or hourly.
Mandate or project
Onboarded within two weeks, then quarterly touchpoints and dedicated points of contact.
Selected references
Excerpts from our references, regulated industry and growing SaaS.
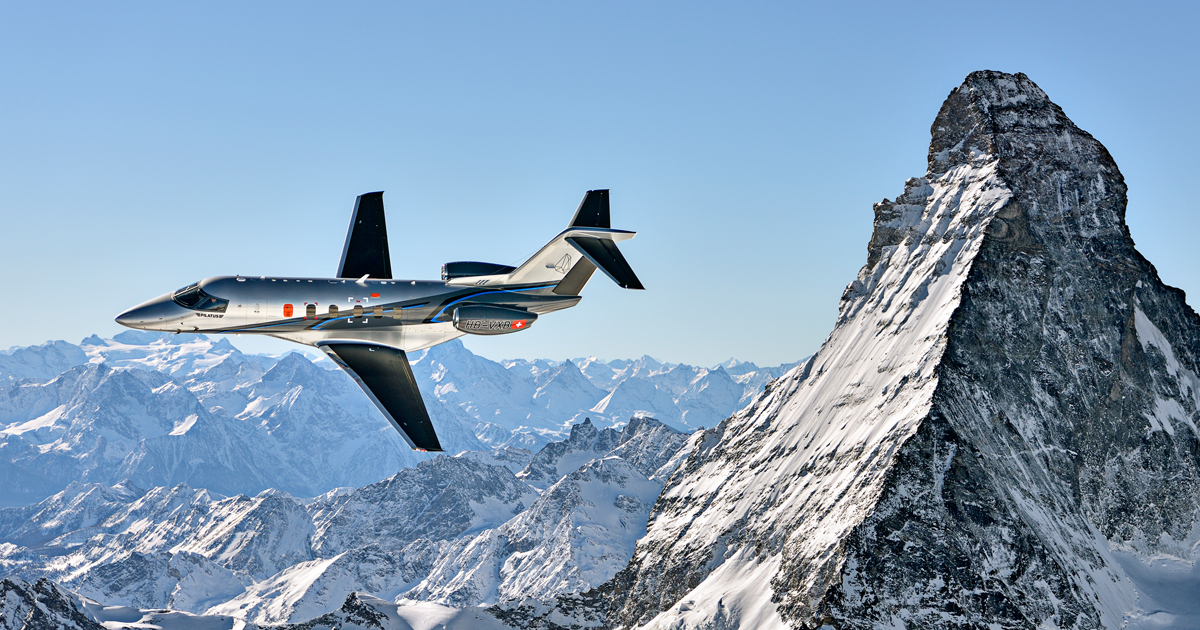
Pilatus Aircraft
Privacy compliance across group boundaries, from ITAR-sensitive processes to international supply chain.
Read case study →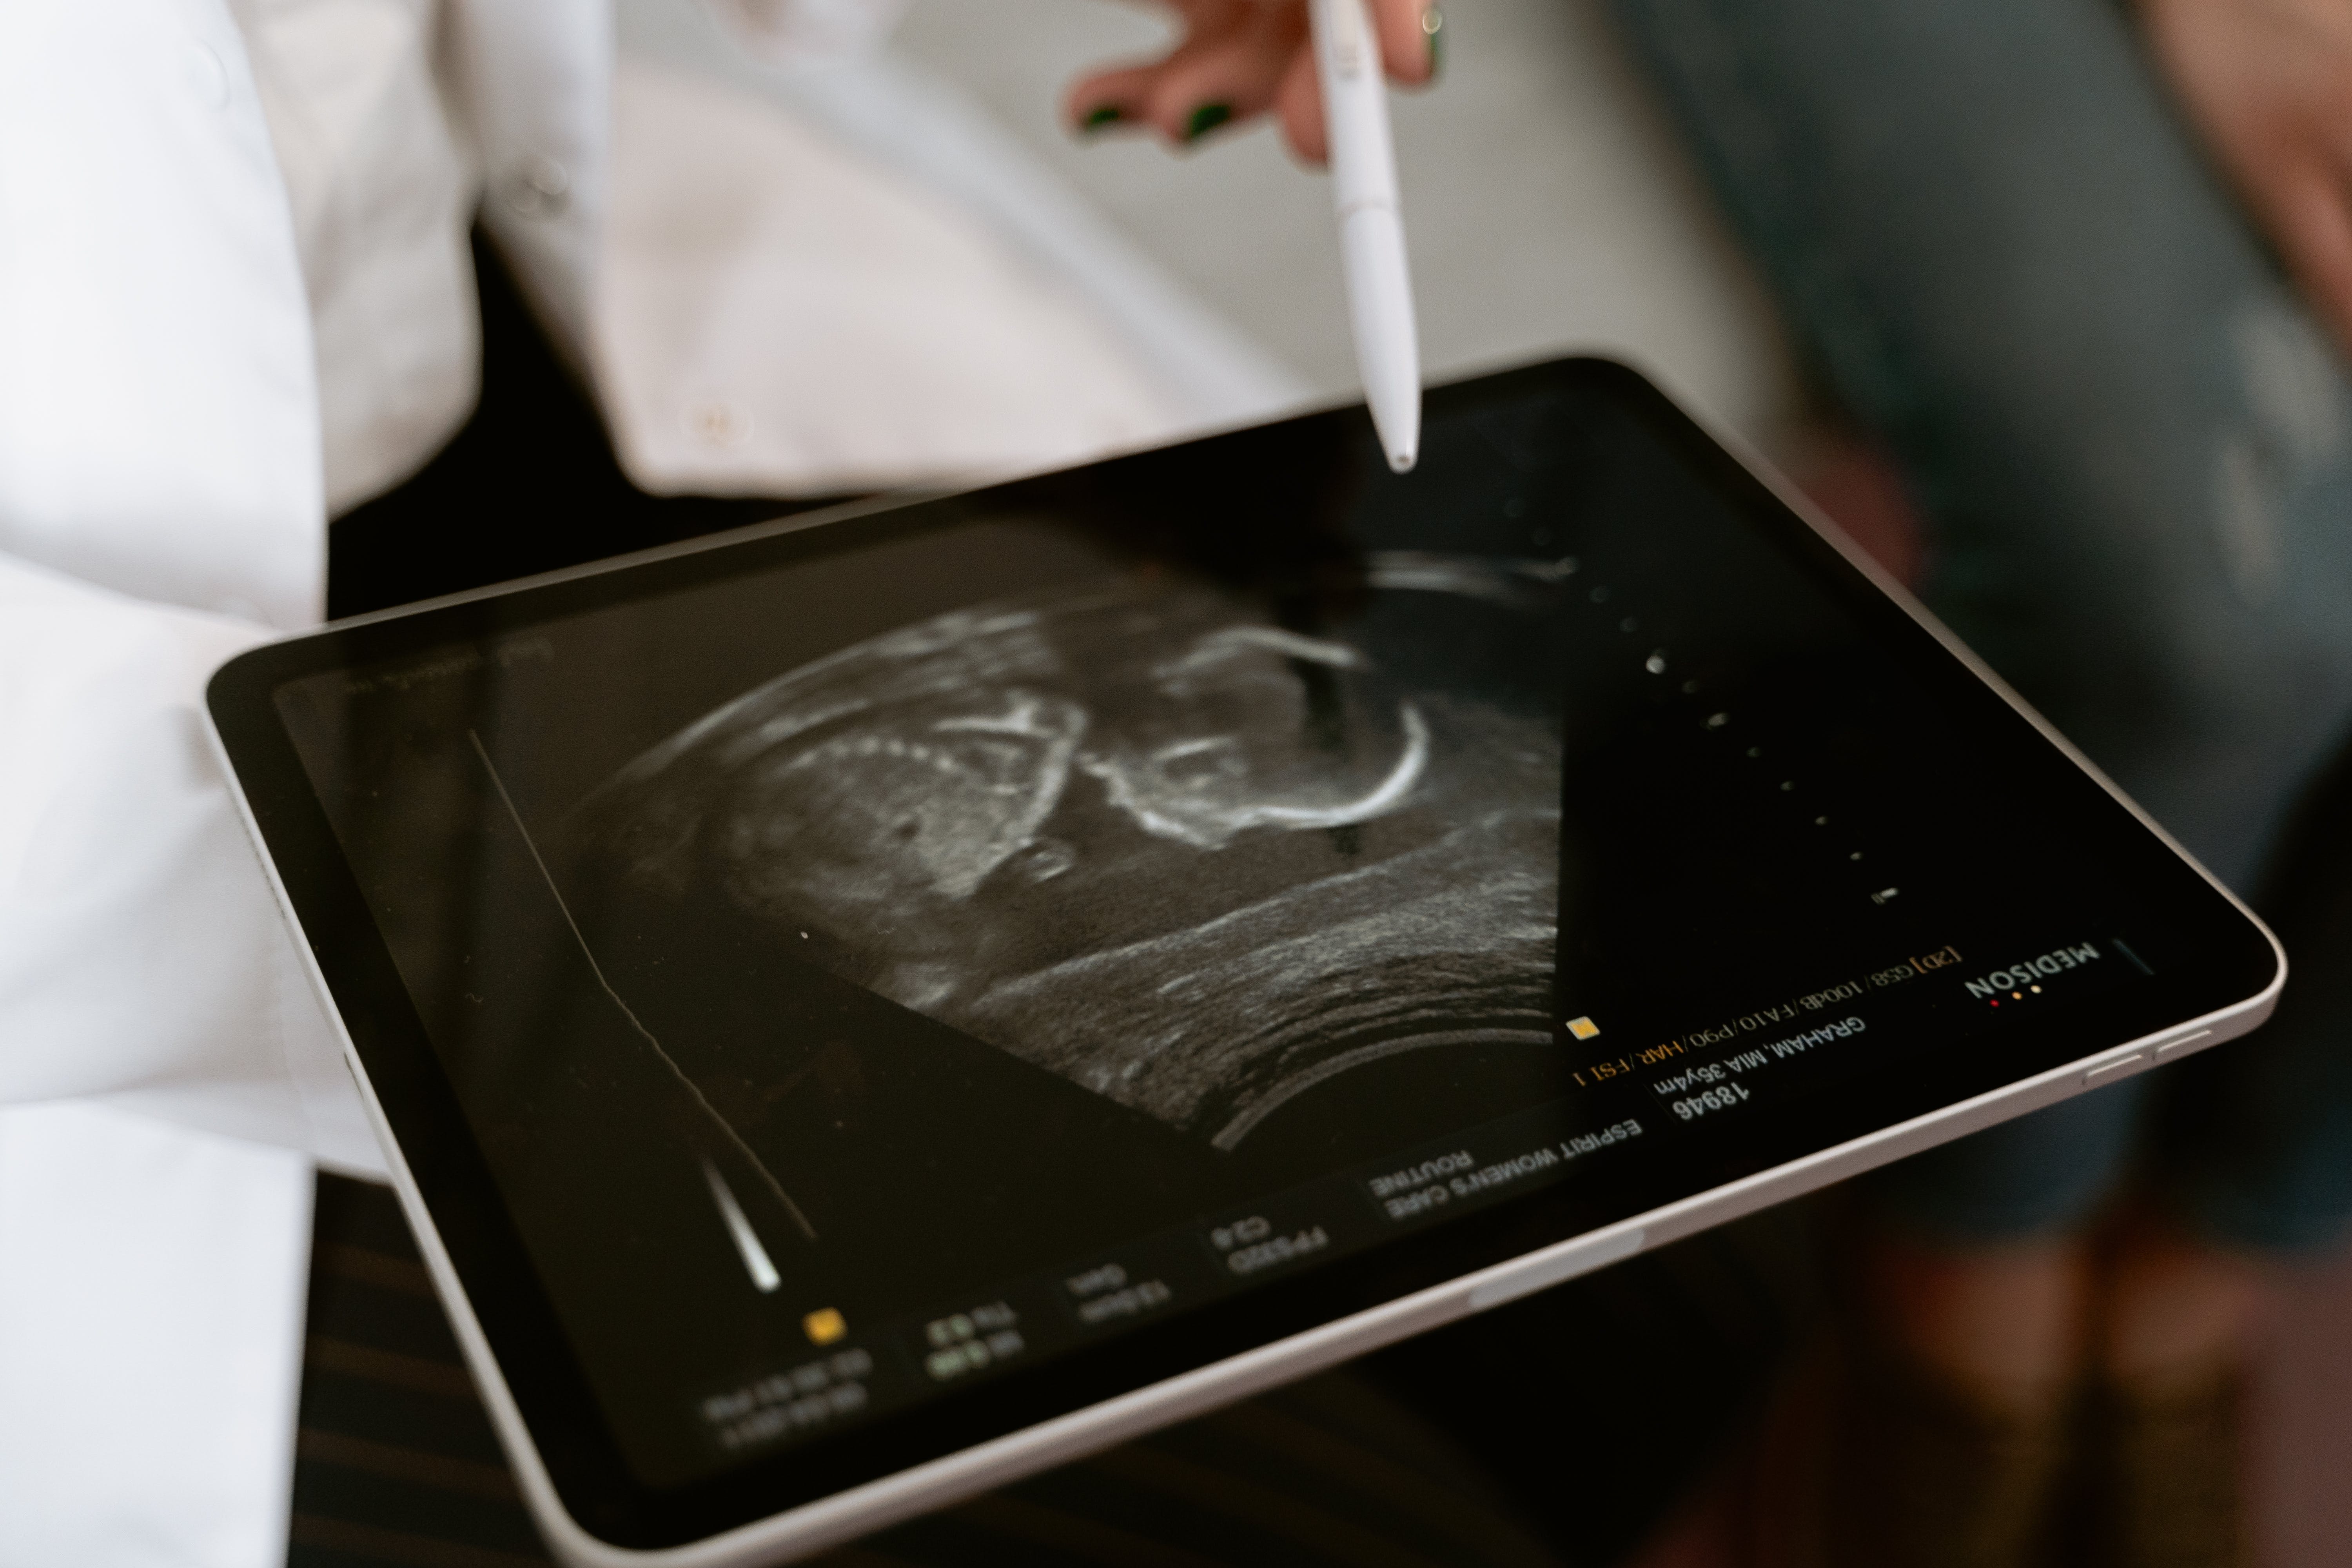
Openmedical AG
Data protection and information security for sensitive patient data in the Swiss electronic patient record (EPR).
Read case study →Frequently asked questions
The answers decision-makers look for before the intro call.
Is the intro call really free and without obligation?
Yes. 30 minutes with Dr. Staiger or a senior consultant, at no cost and with no follow-up obligation. We use the call to understand your situation, you decide afterwards.
We are not based in Switzerland, can you still support us?
Yes. We serve companies in Switzerland, the EU, the UK and the USA. For non-EU companies with EU customers we also act as Art. 27 GDPR representative. Our mandates often cover several jurisdictions at once.
How quickly can you start as external DPO?
Onboarding typically within two weeks after contract. For urgent matters, such as a data breach or regulator request, we are reachable the same or next business day.
Mandate or project, which fits us?
Mandate (e.g. external DPO role) when you need a continuous point of contact, typically CHF 500/month and up. Project when you have a clearly scoped initiative (ISO 27001 build-out, pen test, DPIA, cloud migration). We recommend the right format in the intro call.
Which languages do you work in?
German and English throughout. French and Italian on request. Contracts, expert opinions and training are delivered in the language relevant to your business.
Book an intro call
30 minutes, free, no follow-up obligation. You speak directly with our team.
Prefer to write? Request a quote →